Advertisement
Advertisement
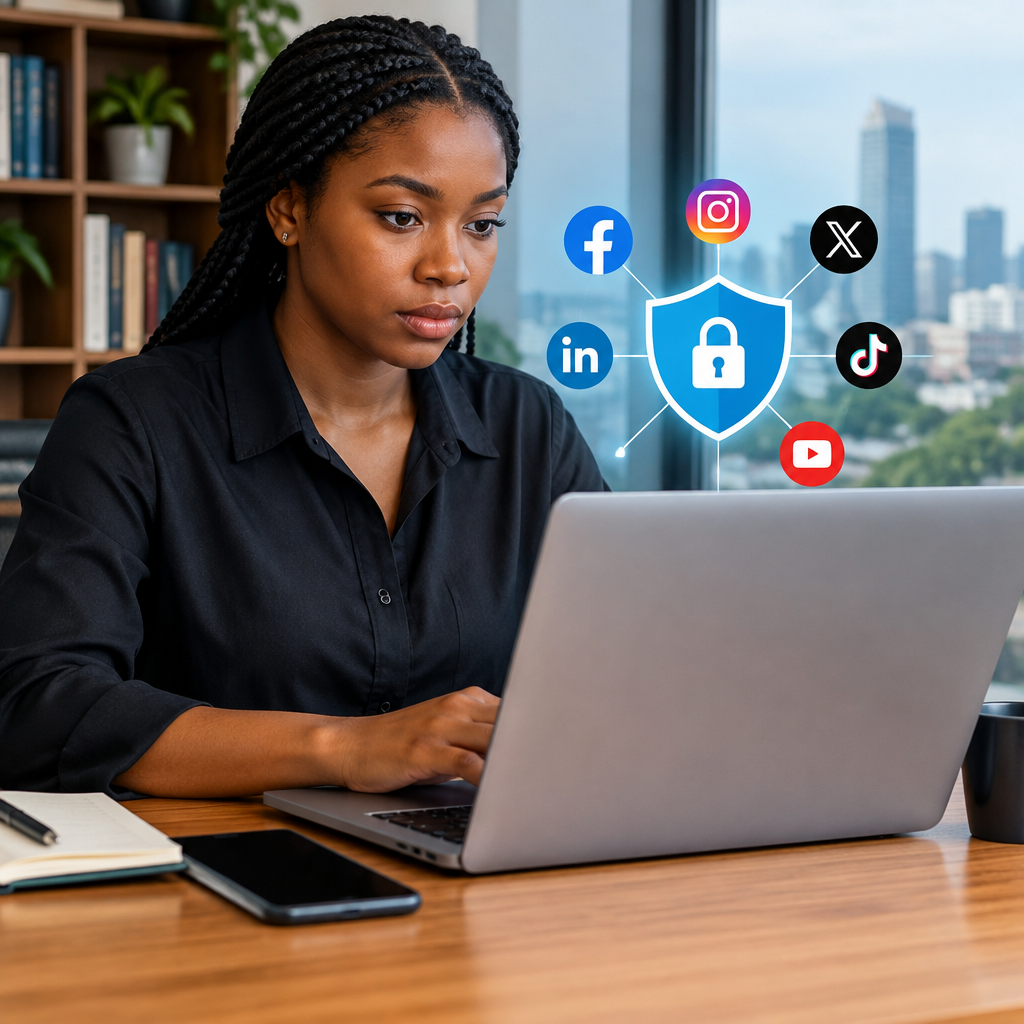
A hacked social media account can quickly become a business crisis. An attacker may change the password, impersonate the business, publish harmful content, scam customers or use saved payment information. For a Nigerian business, creator or online service provider, the damage can also include lost trust and missed sales.
The good news is that most account security improvements do not require advanced technical knowledge. The most important steps are to protect the email address linked to each account, use unique passwords, enable two-factor authentication and control who has access.
Advertisement
Table of Contents
Start with an account security inventory
Before changing settings, list every social media account used by the business. Include active and rarely used profiles, advertising accounts, business pages, creator accounts and accounts connected to shopping or messaging tools.
For each account, record:
- The platform and profile name
- The business email address and phone number linked to it
- Who currently has access
- Whether two-factor authentication is enabled
- Which apps, agencies or scheduling tools are connected
- How the business can recover the account if access is lost
Keep this inventory in a secure password manager or another protected location. Do not store passwords in a public spreadsheet, ordinary chat group or shared note that anyone can open.
Secure the email account first
Your business email is often the master key to social media accounts. If someone controls it, they may request password resets and intercept security alerts. Protect it before protecting the social profiles themselves.
Use a unique password for the email account and enable two-factor authentication. Review its recovery email address, phone number and logged-in devices. Remove old staff, former agencies and unfamiliar devices.
Be careful with email messages that claim your page has violated a policy or that an advertisement needs urgent confirmation. Instead of clicking the link, open the platform’s official app or type its known website address yourself. This helps prevent phishing, where a fake login page captures your password.
Use unique, strong passwords
Every business account should have a different password. Reusing the same password across Facebook, Instagram, TikTok, X, LinkedIn, email and online shopping tools creates a chain reaction: one stolen password can expose several services.
A strong password should be long, difficult to guess and not based on the business name, owner’s name, football club, birthday or phone number. A password manager can create and store different passwords without requiring the team to memorise them.
Never send a password, recovery code, authentication code or private key through a group chat. Platform support staff should not need your password or one-time code to help with a normal account issue.
Turn on two-factor authentication
Two-factor authentication, often called 2FA, adds a second proof of identity after the password. Depending on the platform, this may be an authentication app, security key, text message or another approved method.
An authentication app or physical security key is generally preferable to relying only on text messages, but use the strongest option that the business can manage consistently. The exact settings differ between platforms and devices, so check the account’s official security menu.
When enabling 2FA:
- Set it up from the platform’s official app or website.
- Save the backup or recovery codes in a secure place.
- Do not share those codes in a staff group or with a supposed support agent.
- Make sure at least one authorised business owner can recover the account if the main phone is lost.
- Review which devices and authentication methods are trusted.
Recovery codes are not ordinary login details. Anyone who has them may be able to bypass the second step, so treat them as highly sensitive.
Give people the right access, not the highest access
Businesses often create security problems by sharing one password with everyone. A safer approach is to use the platform’s business or team permissions, where available, and give each person an individual login.
For example, a content editor may need permission to publish posts but not to change the account email, remove the owner or manage payment details. An advertising specialist may need access to campaigns without needing control of the main profile. A web developer or social media agency should receive only the access required for the agreed work.
Review access whenever a staff member changes role, leaves the organisation or finishes a contract. Remove former users promptly. This is particularly important for small businesses, creators and online service providers that work with freelancers or several agencies.
Check connected apps and business tools
Social media accounts are frequently connected to scheduling platforms, analytics tools, online stores, competitions, design services and third-party applications. A connected app may have permission to read information, publish content or manage parts of the account.
Open the platform’s settings and review connected apps regularly. Remove anything the business no longer uses or does not recognise. Before approving a new tool, check:
- Who operates it and whether the website is genuine
- What permissions it requests
- Whether those permissions are necessary
- How access can be revoked later
Do not connect a business account to an unofficial service simply because it promises more followers, free verification or unusually fast growth. Such offers are common routes to stolen credentials and fake engagement.
Protect phones, computers and browsers
Account security also depends on the devices used to access the account. Use a screen lock, keep the operating system and apps updated, and install software only from trusted sources. Avoid logging into business accounts on shared or public computers.
Be cautious when using public Wi-Fi for account administration. If a device is lost, use another trusted device to sign out of active sessions, change important passwords and contact the mobile network provider if the phone number may be at risk.
Do not allow a browser to save business passwords on a computer used by many people. A password manager with a protected vault is safer for team access.
Train the team to recognise scams
Technology cannot prevent every takeover. A team member may receive a convincing message that appears to come from a platform, business partner or manager. The message may demand an urgent login, payment or security code.
Create a simple rule: no employee should provide a password, OTP, recovery code or authentication approval because of an unexpected message. Verify unusual requests through a separate channel, such as a known phone number or an in-person conversation.
Common warning signs include:
- Threats that the account will be deleted immediately
- Requests to click a shortened or unfamiliar link
- Offers of free verification or guaranteed followers
- Requests for payment to restore a profile
- Messages asking for a login code
- Spelling, domain-name or branding inconsistencies
Prepare for a takeover before it happens
Keep evidence that proves ownership of the account, such as the original registration email, business documents where appropriate, invoices for legitimate advertising and screenshots of the profile. Store this information securely and avoid publishing sensitive documents.
Decide in advance who will handle a suspected takeover. The response should include changing the email and account passwords, ending unfamiliar sessions, removing suspicious apps, contacting the platform through its official support route and warning customers through another verified channel.
If an attacker posts a scam, tell customers not to send money or share codes. Do not negotiate with someone demanding payment for account recovery, and do not hire an unknown “hacker” who promises guaranteed restoration.
A practical monthly security routine
Once a month, the account owner or security lead should:
- Review logged-in devices and active sessions
- Check administrators, editors and other assigned roles
- Remove unused connected apps
- Confirm that 2FA and recovery details still work
- Look for unusual posts, messages, adverts or profile changes
- Check that the linked email account remains secure
Run an additional review whenever someone leaves the business, a phone is lost, a suspicious link is opened or an unfamiliar login alert appears.
The most important security decision
Business social media security is not only about choosing a stronger password. It is about limiting access, protecting recovery channels and creating a clear response when something goes wrong. A Nigerian news platform, online shop, creator programme or web service provider can all use the same basic approach: secure the email, enable 2FA, assign individual permissions, review connected tools and train everyone who handles the account.
Take these steps one account at a time. A short security review today can prevent a much larger business, reputation and customer-trust problem later.
Advertisement